AI Gateways Under Fire: Attackers Chain LiteLLM and MCP Flaws for Remote Code Execution
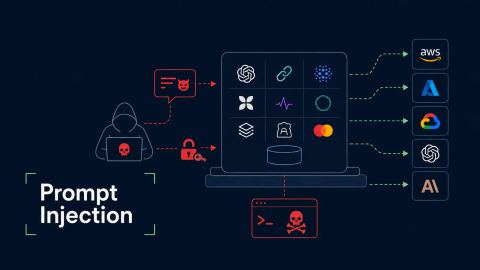
A 90-day honeypot study shows attackers systematically probing AI proxies, MCP servers, and agent frameworks like LangChain and Langflow, chaining authentication bypass and command-injection bugs into remote code execution, credential theft, and cryptomining. Researchers say a single misconfigured AI gateway can expose model API keys and cloud permissions for an entire organization. The post AI Gateways Under Fire: Attackers Chain LiteLLM and MCP Flaws for Remote Code Execution appeared first on Secure Bulletin.
Itagora tiene in archivio titolo e sommario per la ricerca interna. Il testo completo resta sulla fonte. Il link in uscita non invia referrer.