Infostealers Target Claude Sessions, Letting Attackers Bypass MFA and Drain Paid Accounts
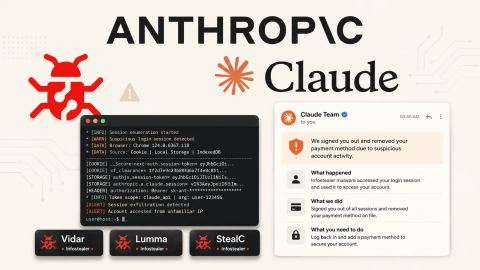
Attackers are stealing authenticated Claude browser sessions and abusing malicious ads and files to compromise users. Anthropic has invalidated affected sessions and refunded confirmed charges, but victims must remove the underlying malware before signing in again. The post Infostealers Target Claude Sessions, Letting Attackers Bypass MFA and Drain Paid Accounts appeared first on Secure Bulletin.
Itagora tiene in archivio titolo e sommario per la ricerca interna. Il testo completo resta sulla fonte. Il link in uscita non invia referrer.